Eliminate Cloud Dependency for Visual Design
Most creative professionals trust their secrets to massive cloud providers today. This reliance creates a dangerous vulnerability for proprietary architectural data and private sketches.
The modern tech landscape is plagued by subscription traps and privacy leaks. You need a sanctuary where your visual ideas remain completely under your control.
Disclaimer: I may earn a commission from purchases made through these links at no extra cost to you.


The Experience of Local Sovereignty
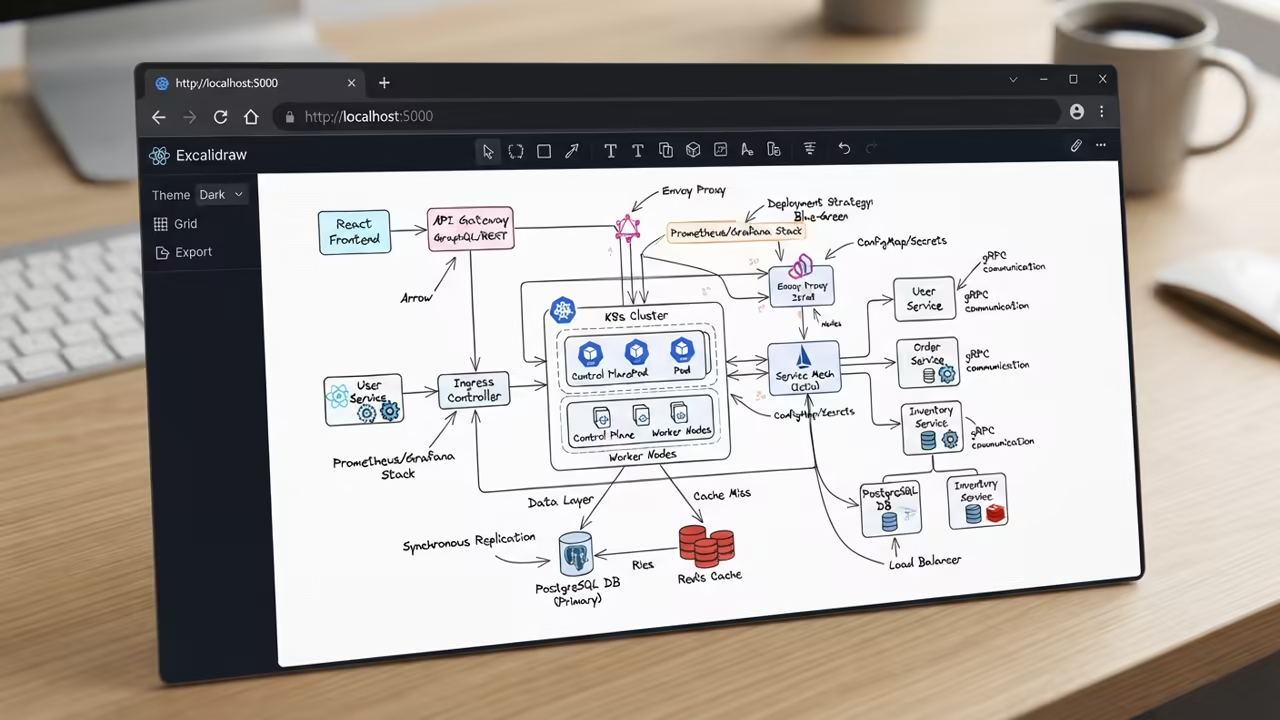
The moment your local whiteboard flashes onto the screen is pure liberation. You finally own every single pixel of your creative process without external trackers.
It feels like unlocking a hidden superpower for your local workstation. Your designs load instantly because the data never leaves your own physical hardware.
Deploying the Rootless Stack
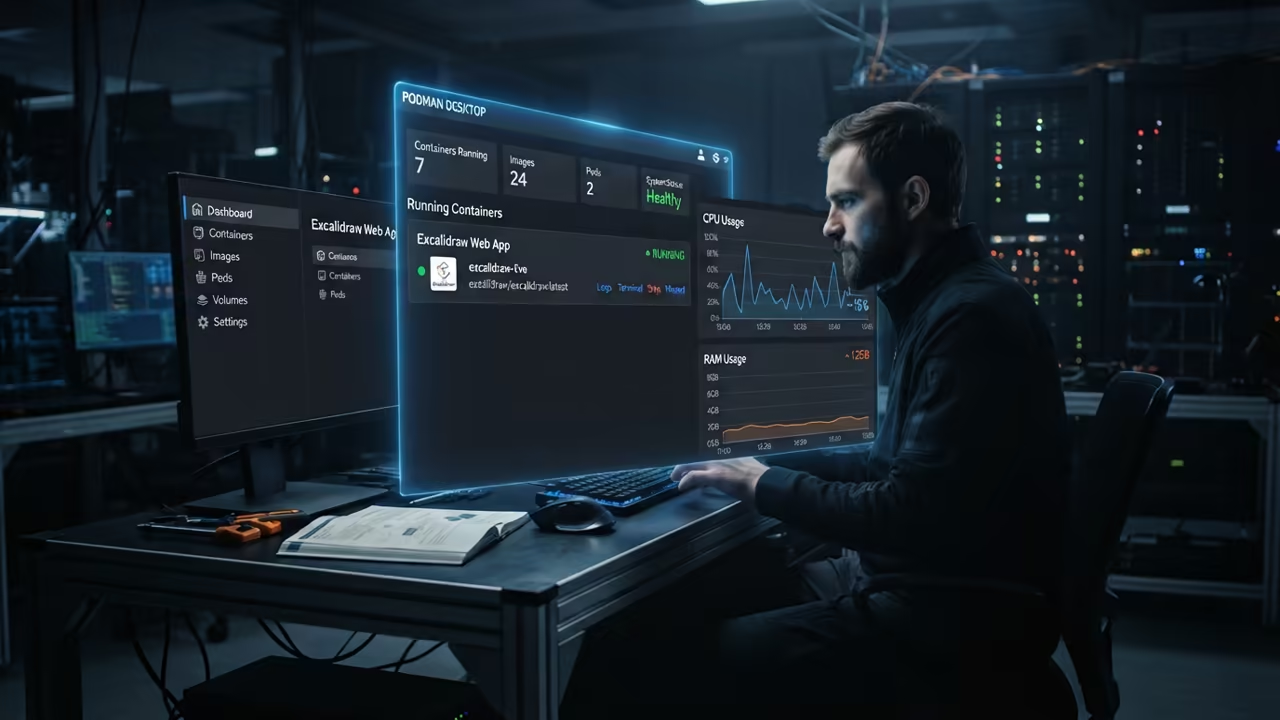
Start by installing Podman Desktop to manage your containerized environments easily. This tool streamlines the setup of the underlying Linux virtual machine automatically.
The interface allows you to monitor resource usage in real time. You can deploy complex environments without ever touching a complex command line interface.
To launch your private instance use the following command in your terminal. This pulls the official image and maps the port for immediate local access.
podman run --rm -dit --name excalidraw -p 5000:80 excalidraw/excalidraw:latest
Once the container is active you can access the tool via localhost. Your browser now serves a professional grade whiteboard hosted on your own machine.
Advanced Configuration Secrets
To achieve professional grade deployment you should utilize the Pod concept. Grouping Excalidraw with a Caddy container allows for effortless SSL termination.
This insider trick prevents the browser from complaining about insecure local connections. It mimics a production environment while maintaining the security of rootless execution.
Security Architecture Breakdown
Rootless containers provide a massive security advantage over traditional daemon based systems. Your host system remains isolated even if the container is compromised.
This architecture follows the principle of least privilege for all local users. It eliminates the need for dangerous root escalation during the deployment process.
This approach connects directly to our previous deep dives on secure home labs. You can integrate this setup into a larger autonomous architectural framework.
| Parameter | Description | Value |
|---|---|---|
| Security | Rootless Default | Podman |
| Security | Root Required | Docker |
| Architecture | Daemonless | Podman |
| Architecture | Client Server | Docker |
| Resource Use | Low Overhead | Podman |
| Resource Use | Higher Overhead | Docker |
| Parameter | Description | Value |
Maintaining your own tools is the only way to ensure long term stability. You are no longer subject to the whims of corporate pricing changes.
This setup transforms your machine into a powerhouse of private creative production. The speed and security of Podman make it the obvious choice.
Learning and Support
Reach out for personalized technical help to optimize your container stack. Dive deeper into these secrets with our comprehensive online tutorial series.
- Online Tutorials & Technical Help: https://ojambo.com/contact
🚀 Recommended Resources
Disclosure: Some of the links above are referral links. I may earn a commission if you make a purchase at no extra cost to you.
Leave a Reply